Engager des journalistes

Éditeurs et diffuseurs Équipes de marketing de contenu Équipes RP et communication Équipes risques et renseignement Trouver des journalistes Veille médias Tarifs

Pour les journalistes

Offres d'emploi en journalisme Tarifs Créez votre profil gratuit

À propos de Shakhawat

Travaux 34

TryHackMe — Tomghost Exploitation

Medium 5 févr. 2025 English

A penetration-testing walkthrough of the TryHackMe Tomghost machine. Scanning identified Apache Tomcat 9.0.30 and the GhostCat vulnerability, which exposed SSH credentials for the skyfuck account. The writer then recovered a GPG passphrase, accessed the merlin account, exploited passwordless sudo permission for zip, and gained root access to retrieve the user and root flags.

Cybersecurity Penetration Testing Vulnerability Exploitation Privilege Escalation Capture the Flag TryHackMe Shakhawat Hossain Apache Tomcat Metasploit Nmap John the Ripper GNU Privacy Guard
Style rédactionnelFactuel

Highly factual and procedural, documenting commands, vulnerabilities and exploitation results.
TryHackMe — Tomghost Exploitation

Medium 5 févr. 2025 English

A walkthrough of exploiting the TryHackMe Tomghost machine begins with Nmap discovery of SSH, Apache JServ, and Apache Tomcat services. The author exploits the GhostCat vulnerability in Tomcat to retrieve SSH credentials, accesses the system as skyfuck, cracks a GPG-related passphrase to obtain merlin’s credentials, and then abuses merlin’s passwordless sudo permission for the zip utility to escalate to root. The process yields the user flag and root flag.

Penetration Testing Cybersecurity Vulnerability Exploitation Privilege Escalation Shakhawat Hossain TryHackMe Apache Tomcat Metasploit Nmap John the Ripper OpenSSH GnuPG
Style rédactionnelFactuel

Predominantly factual and procedural penetration-testing walkthrough with minimal subjective commentary.

CyberBangla CTF Writeups | Primary CTF

Medium 1 févr. 2025 English

Shakhawat Hossain documents solutions to challenges from Cyber Bangla’s Primary CTF, where he placed third among more than 120 participants. The writeup covers cryptographic decoding and hash cracking, web vulnerabilities and source-code analysis, cookie manipulation, steganography, and OSINT techniques. Tools including CyberChef, John the Ripper, dcode.fr, Burp Suite, and GitHub commit history were used to recover flags from challenges involving Base64, zero-width Unicode, SHA-256 and MD5 hashes, PHP behavior, encrypted cookies, image metadata, and a public repository.

Capture the Flag (CTF) Cybersecurity Web Penetration Testing Cryptography Steganography Open-Source Intelligence Bangladesh Cyber Bangla Cyber Bangla Academy Shakhawat Hossain Naruto Pain
Style rédactionnelInformatif

Primarily factual and instructional, with some personal reactions and subjective commentary about the challenges.

Seed Dormancy and Germination Potential of Coastal Rice Landraces in Bangladesh: Implications for Climate-Resilient Cultivation

Sustainability 15 janv. 2025 English

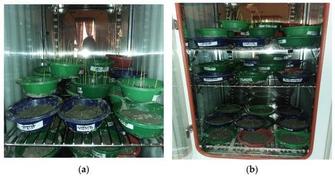
The study investigates the seed dormancy and germination potential of 28 local Aman rice landraces and four varieties from Bangladesh's coastal regions, highlighting their importance for climate-resilient agriculture. The research identifies significant genetic variability in seed dormancy among these landraces, with some exhibiting high dormancy rates, making them suitable for cultivation in disaster-prone areas. The findings suggest that these genotypes can be used in breeding programs to develop pre-harvest sprouting-resistant varieties, offering potential solutions for sustainable rice cultivation in Bangladesh's coastal regions.

Seed Dormancy Germination Climate-Resilient Cultivation Rice Landraces Bangladesh Australia Canada Bangladesh Institute of Nuclear Agriculture Bangladesh Rice Research Institute Patuakhali Science and Technology University Northwest Agriculture and Forest University The University of Sydney
Style rédactionnelFactuel

The article is based on scientific research and presents factual data and analysis.

The Sticker Shop | TryHackMe | Walkthrough

Medium 30 nov. 2024 English

A walkthrough of TryHackMe’s The Sticker Shop challenge, which involves exploiting a Blind XSS vulnerability in a customer feedback form. The author confirms JavaScript execution using Burp Collaborator, then uses a crafted payload to fetch a flag from the target’s localhost service and exfiltrate it to a listener. The challenge demonstrates the risks of unsanitized user input and the importance of input validation and output escaping.

Cybersecurity Web Application Security Cross-Site Scripting Capture the Flag Penetration Testing TryHackMe Shakhawat Hossain Burp Collaborator
Style rédactionnelFactuel

Predominantly factual technical walkthrough with limited subjective commentary.

The Sticker Shop | TryHackMe | Walkthrough

Medium 30 nov. 2024 English

A walkthrough of the TryHackMe Sticker Shop challenge, in which a feedback form is exploited through Blind XSS. The author identifies that submitted feedback is reviewed in a staff browser, confirms JavaScript execution with Burp Collaborator, and uses a crafted payload to fetch a flag from the reviewer’s localhost service and send it to an external Python HTTP server. The challenge demonstrates the risks of unsanitized user input, Blind XSS, and insecure handling of locally accessible sensitive data.

Web Application Security Cross-Site Scripting Penetration Testing Capture the Flag Shakhawat Hossain TryHackMe Burp Collaborator Python HTTP Server
Style rédactionnelInformatif

Primarily factual and instructional, with limited personal commentary about the exploitation process.

Vulnerabilities 101 — Writeup | TryHackMe

Medium 15 sept. 2024 English

An introductory TryHackMe walkthrough explains what cybersecurity vulnerabilities are, how they are classified, and how CVSS and Tenable’s VPR frameworks assess their severity and organizational risk. It introduces the National Vulnerability Database and Exploit-DB as research resources, then demonstrates using version disclosure to identify Apache Tomcat and locate applicable exploits. The practical engagement concludes with the recovery of the flag THM{ACKME_ENGAGEMENT}.

Cybersecurity Vulnerability Research Penetration Testing Vulnerability Scoring Exploit Databases NIST OffSec ACKme IT Service ThePentestingCo Shakhawat Hossain TryHackMe Tenable
Style rédactionnelFactuel

Predominantly factual and instructional, presenting cybersecurity concepts, frameworks, databases, and a practical exploitation walkthrough.

Week 1 Recap: Building the Foundation for PNPT Success!

Medium 19 mai 2024 English

Shakhawat Hossain recaps the first 12 days of a PNPT preparation journey, focusing on networking fundamentals such as IP and MAC addresses, three-way handshakes, and subnetting. He also established a virtual lab with VMware or VirtualBox and Kali Linux, and began learning Bash scripting and Python fundamentals. Detailed daily notes were published in a GitHub repository, with plans to apply these foundational skills to practical scenarios in later weeks.

Penetration Testing Cybersecurity Education Networking Fundamentals Linux Programming Shakhawat Hossain VMware Kali Linux VirtualBox Bash scripting Python
Style rédactionnelÉquilibré

Personal learning recap with enthusiastic and subjective language, while primarily describing factual study activities and technical concepts.

Week 1 Recap: Building the Foundation for PNPT Success!

Medium 19 mai 2024 English

Shakhawat Hossain recaps the first stage of his PNPT preparation, which took 12 days rather than the planned seven because of participation in cybersecurity workshops and CTFs. He studied IP and MAC addressing, TCP three-way handshakes, subnetting, virtual-machine setup, Kali Linux, Bash scripting, and Python fundamentals. Detailed daily notes were uploaded to GitHub, and he plans to apply these foundational skills to practical penetration-testing scenarios in later weeks.

Penetration Testing Cybersecurity Education Networking Fundamentals Linux Python Programming Shakhawat Hossain PNPT VMware VirtualBox Kali Linux Bash Python
Style rédactionnelInterprétatif

Personal learning recap with enthusiastic and subjective commentary, grounded in a factual account of completed study topics.

Cracking the PNPT: My Journey to Mastering Penetration Testing!

Medium 7 mai 2024 English

Shakhawat Hossain announces his plan to pursue the Practical Network Penetration Tester certification and document the process. He intends to share weekly learning summaries on LinkedIn and detailed daily notes, resources, and exploits through GitHub, inviting others to follow and participate in discussions about penetration testing and cybersecurity.

Penetration Testing Cybersecurity Education Professional Certification Shakhawat Hossain Practical Network Penetration Tester (PNPT) certification
Style rédactionnelÉquilibré

Personal announcement with subjective enthusiasm and goals, alongside factual information about the planned learning process.

Voir les 34 réalisations avec un compte gratuit

Recruter Message
×

Inscrivez-vous pour envoyer un message à Shakhawat

Vous avez déjà un compte ? Se connecter
Vous cherchez du travail ? S'inscrire en tant que journaliste
Vérifiez votre e-mail pour finaliser l'inscription
Nous venons d'envoyer un e-mail à . Veuillez consulter votre boîte de réception et cliquer sur le lien pour vérifier votre adresse e-mail et finaliser votre inscription. Si vous ne voyez pas l'e-mail, pensez à vérifier votre dossier spam ou courrier indésirable.
Vous n'avez pas reçu l'e-mail ?

Inscrivez-vous pour débloquer les profils

Vous avez déjà un compte ? Se connecter
Vous cherchez du travail ? S'inscrire en tant que journaliste
Vérifiez votre e-mail pour finaliser l'inscription
Nous venons d'envoyer un e-mail à . Veuillez consulter votre boîte de réception et cliquer sur le lien pour vérifier votre adresse e-mail et finaliser votre inscription. Si vous ne voyez pas l'e-mail, pensez à vérifier votre dossier spam ou courrier indésirable.
Vous n'avez pas reçu l'e-mail ?